


Feedback

Last date modified: 2026-Oct-02
You can manage permissions more efficiently using the Features tab. Instead of adjusting individual settings across Object Security, Tab Visibility, and Other Settings, you can enable permissions by feature.
Features represent key system capabilities such as Preservation, Production, Imaging, and Configure Doc Review. Each feature groups together the necessary permissions from the three tabs. When you enable a feature, all related permissions are automatically applied.
To achieve this, all permission changes must now be made through Feature Permissions instead of the older granular settings in Object Security, Tab Visibility, and Other Settings/Admin Operations. The modernization of Feature Permissions simplifies permissions management and creates consistency across workflows. This update ensures that feature behavior is standardized and easier for end users to understand and use.
Feature Permissions are rolling out through a phased modernization. Migration tooling supports controlled adoption with full audit visibility.
During migration, each feature exists in one of two states:
When you enable or disable a feature, Feature Permissions applies or revokes the entire set of dependent permissions in a single action. This simplifies configuration and reduces the risk of misaligned settings.
Below you will find the current Feature Permissions that are modernized. When a feature is modernized, its associated Object Security, Tab Visibility, and Admin Operations permissions are locked and can only be modified through the Feature Permission toggle. For more information, see Modernized features.
 = Shared granular permission
| Modernized Feature Permission | Level | Object Security | Tab Visibility | Admin Operations / Other |
|---|---|---|---|---|
| aiR Review | Instance | None | aiR Review Jobs |
View Admin Repository |
| Application Management | Instance |
Library Application – View OAuth2 Client – View, Add, Edit, Delete, Secure Resource File – View, Add, Edit, Delete, Secure Custom Page – View, Add, Edit, Delete, Secure Sanitizer – View, Add, Edit, Delete, Secure
|
Application Library
OAuth2 Client Resource Files Custom Pages Sanitizer
Relativity Script Library |
View Admin Repository |
| Archive and Restore (ARM) | Instance | None |
ARM ARM Jobs Configuration |
View Admin Repository |
| Audit | Instance |
Data Grid Audit – View
|
Audit
Audit Migration Reports |
View Audits
|
| Authentication | Instance |
Group Claim Mapping – View, Edit, Add, Delete, Secure Required Claim – View, Edit, Add, Delete, Secure JIT Settings – View, Edit, Add, Delete, Secure Federated Instance – View, Edit, Add, Delete, Secure |
Authentication Provider Authentication Provider (legacy) Authentication Provider Type Federated Instance |
View Admin Repository |
| Case Metrics | Instance |
Schedule – View, Edit, Add ScheduleReport – View, Edit, Add ScheduleReportField – View, Edit, Add ScheduleReportFilter – View, Edit, Add |
Case Metrics Reports Scheduler |
View Admin Repository |
| Client and Matter Management | Instance |
Client – View, Edit, Add, Delete, Secure Matter – View, Edit, Add, Delete, Secure |
Clients Matters |
View Admin Repository |
| Cost Explorer | Instance | None |
Cost Explorer
|
View Cost Explorer |
| Data Transfer | Instance | None | Staging Explorer |
Access Staging Explorer Send Email Notification |
| Instance Configuration | Instance |
View – View, Edit, Add, Delete, Secure Field – View, Edit, Add, Delete, Secure + Add Field Choice By Link Object Type – View, Edit, Add, Delete, Secure Object Rule – View, Edit, Add, Delete, Secure Layout – View, Edit, Add, Delete, Secure Tab – View, Edit, Add, Delete, Secure Choice – View, Edit, Add, Delete, Secure Dashboard – View, Edit, Add, Delete, Secure Agent – View, Edit, Add, Delete, Secure Agent Type – View, Edit, Add, Delete, Secure InstanceSetting – View, Edit, Add, Delete, Secure |
Admin Workspace Configuration Views Fields Object Type Choices Dashboards Tabs Tab Sync Agents Server & Agent Management Instance Settings |
Delete Object Dependencies Manage Object Types Agent Operations |
| Job Queues | Instance | None |
Queue Management OCR Queue PDF Queue Processing and Imaging Queue DtSearch Queue Admin Import/Export Queue Branding Queue Branding Queue Legacy Production Queue Production Queue Legacy Processing Administration Processing History Translate Jobs kCura Admin Workspace Upgrade Queue Text Migration Jobs Text Migration Reports Transcription Queue |
Change Queue Priority |
| Migrate | Instance |
Migrate Migration – View, Edit, Add, Delete, Secure Migrate Restore Job – View, Edit, Add, Delete, Secure |
Migrate |
Access Migrate |
| Security Center | Instance | None | Security Center | None |
| Staging Reports | Instance | None |
Staging Reports
|
View Instance-wide Staging Reports View Client Domain Staging Reports |
| Usage Reports | Instance | None |
Management Console |
View Instance-wide Usage Reports View Client Domain Usage Reports |
| Users and Groups Management | Instance |
User – View, Edit, Add, Delete, Secure Group – View, Edit, Add, Delete, Secure
|
Groups Users
Centralized Authentication User Status |
Send Message Force Logout on User Status |
| Workspace Management | Instance |
Workspace – View, Edit, Add, Delete, Secure
Matter – View, Add Resource Pool – View |
Workspaces |
Manage Cold Storage |
This table is updated as additional features move to the modernized state. Check back regularly or review the release notes for the latest changes.
Keep these factors in mind when setting Feature permissions:
The Features tab lists the features available for the selected group. Each feature shows its current state for that group.
To apply a preset to a feature:
Some features control only a few permissions and do not offer presets. Select the checkbox next to the feature to grant access. Clear the checkbox to remove access.
You can also do the following from the Features tab:
Actions are available within Feature Permissions. An action represents a specific task that users can perform within a feature. Actions allow administrators to customize access for a group by granting only the tasks they need instead of granting access to the entire feature.
Example: the Audit feature includes two actions: View Audit and View Audit Migration Reports.
Key details about actions:
A preset is an optional group of related actions. It gives you a starting point for a feature. When you select a preset, Relativity selects the actions defined for that preset. You can then select or clear individual actions before you save.
Most features with presets offer Viewer and Administrator. Staging Reports and Usage Reports offer Client Domain and Instance-wide. Some features have no preset. For those, select all actions, or select individual actions.

A feature’s state for a selected group depends on how many actions are enabled:


A feature with no actions has only two states: Disabled or Enabled.
Some features map their actions to granular permissions. To see this mapping, open the feature's See details panel. Click Granular permissions mapping. The mapping is a read-only reference. It shows the granular permissions behind each preset or action.
The mapping uses these icons:


Feature permissions and granular permissions represent the same access from different perspectives. How changes are applied depends on whether the feature has been modernized.
These behaviors apply to every feature, whether or not it is modernized:
A modernized feature locks its granular permissions, so you cannot change them directly. Changing a granular permission is therefore the one behavior that applies only to features that are not modernized.
For non-modernized features, access can be managed from either the Features tab or the Object Security, Tab Visibility, and Other Settings tabs. The standard feature behaviors described above still apply. You can also enable or disable granular permissions directly. When you do, the state of every enabled feature that includes that permission is updated. A feature is considered enabled only when all of its associated permissions are enabled.
Keep the following behaviors in mind:
As features move to the modernized state, the way you manage permissions for them changes. The Features tab becomes the only way to change access. The feature permission is its own entity rather than a collection of the granular permissions behind it. Relativity locks those granular permissions and manages them, so you cannot change them on the Object Security, Tab Visibility, or Other Settings tabs. Only the behaviors for all features apply.
Legacy granular permission pages, such as Object Security, show a banner directing you to make permission changes on the Features tab.
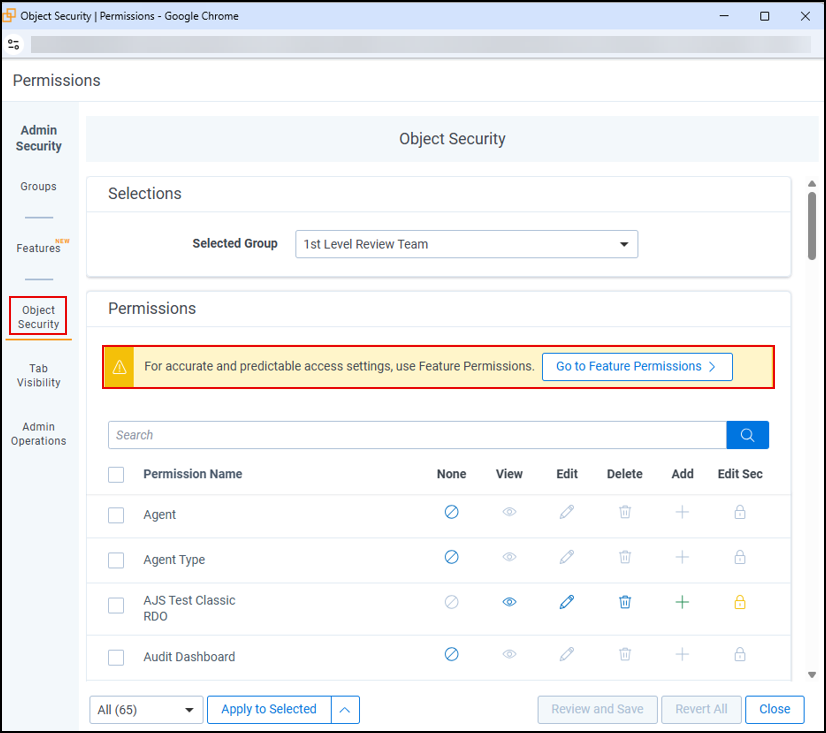
Whether you can change a granular permission depends on the features it belongs to:
| Granular permission | Feature state | Can you change it |
|---|---|---|
| Not modernized—belongs to no modernized feature | Any | Yes |
| Fully modernized—belongs only to modernized features | Any | No |
| Partially modernized—belongs to both modernized and non-modernized features | At least one modernized feature is enabled | No |
| All modernized features are disabled | Yes |
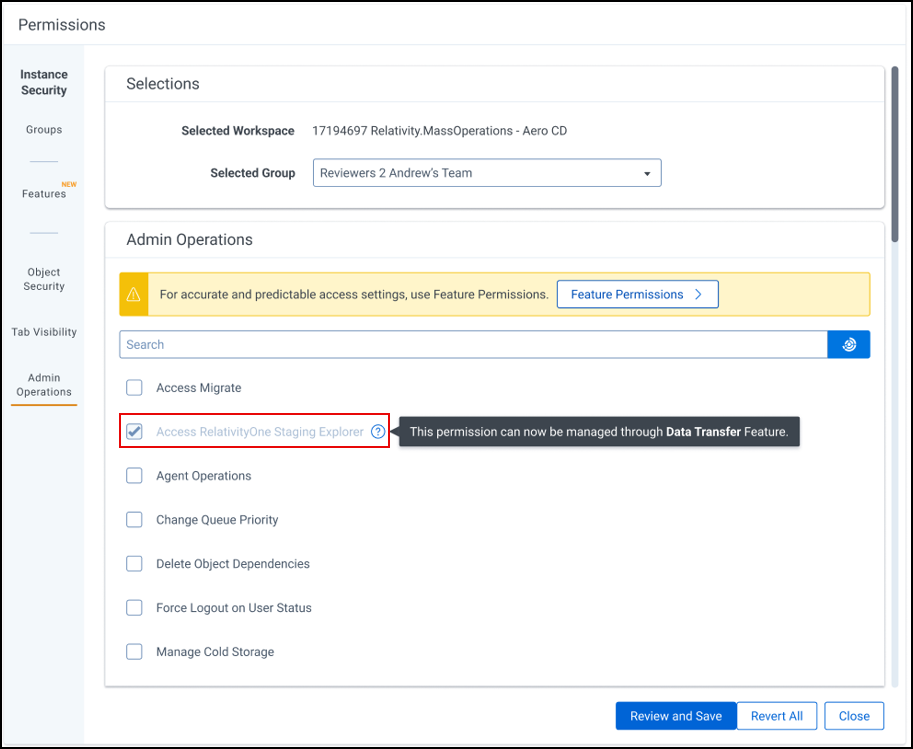
A fully modernized granular permission is read-only. A tooltip names the feature permission to use instead.
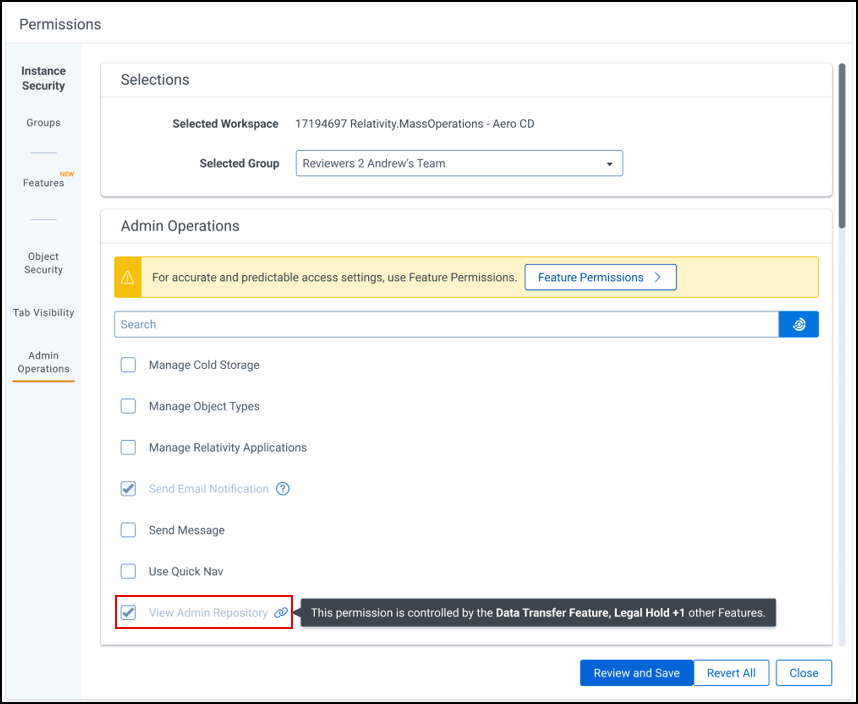
A partially modernized granular permission is read-only while at least one of its modernized features is enabled. A message names the feature permissions that require it.
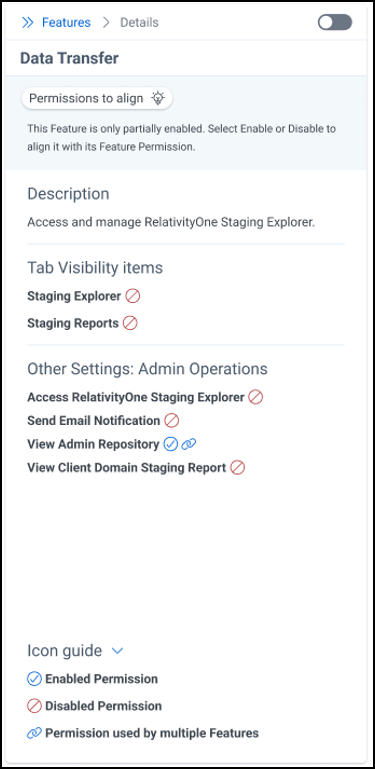
A granular permission shared across multiple features does not always reflect the state of any one of them. The See details panel lists every granular permission a feature includes, and a blue link icon marks the shared ones.
 Will I be able to continue to use granular permissions for certain use cases?
No, if the feature is modernized, management can only be done via the feature permission. If the feature has not been modernized granular permissions can be leveraged to manage the permissions.
What is the difference between a modernized and non-modernized Feature Permission?
A modernized Feature Permission is the sole control point for granting or revoking access to that feature. The underlying granular permissions are locked and managed automatically. A non-modernized Feature Permission works as it does today. You can still edit granular permissions directly on the Object Security, Tab Visibility, and Other Settings tabs.
What does the blue lightbulb icon mean?
The blue lightbulb icon indicates that a group's current permissions configuration is out of alignment with a modernized Feature Permission. You should enable or disable the feature to bring the group into alignment. See Aligning permissions with modernized features for steps.
Do I need to take action immediately when a feature is modernized?
Existing groups and their permissions configurations are not impacted at the time of modernization. However, it is highly encouraged to align each group's permissions as soon as possible so that they are prepared for the future state of permissions.
Why is the user not seeing a tab that should be available as part of the enabled feature?
Why are certain features not available in my workspace?
I had enabled a Feature for a specific group earlier, but now it appears as disabled for that same group. What could have caused this?
Set administrator or user permissions at the feature level. The tables below show the specific permission settings included in each feature at the workspace-level.
For more details on setting feature permissions, refer to Setting workspace permissions.
None stands for Not Applicable
Automated workflows
Purpose: Automates multi-step processes in a workspace. For example, running searches, imaging sets, or productions in sequence without manual intervention. With this feature enabled, a group can create and manage Automated Workflow objects (the definitions of the workflows) and access the Automated Workflows tab.
Permissions:The feature grants full rights to the Automated Workflows object (Add, Edit, Delete, etc., including “Copy to Workspaces” and “Sync to Workspaces”) so users (typically admins or power users) can design workflows. It also ensures the group has any needed rights for actions the workflows might perform. For example, rights to run imaging sets, OCR sets, dtSearch indexes, search term reports, and structured analytics sets if those are part of a workflow. The feature toggle also exposes the Automated Workflows tab in the workspace UI and enables special mass operations (like “Set Long Text Field Size”) that certain automated actions require.
Considerations: Only administrative users should typically have this feature, since designing workflows requires broad access to many objects. When the feature is enabled, the system adds a dedicated backend “Workflow Agent” user to run workflow actions. The designing user must have all necessary rights, but the actions execute under that agent account.
The feature permissions designated for Automated workflows are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| Administrator | Automated workflows - Add, Edit, Delete, View, Secure, Copy to Workspaces, Sync to Workspaces | Admin | None |
Case metrics
The feature permissions designated for Case metrics are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| User | Reviewer Metrics - View, Add, Edit, Delete, Secure | Case Metrics | View All Audits |
| Reports | |||
| Reviewer Metrics |
Collect
The feature permissions designated for Collect are:
| Role (Admin or User) | Object Security | Tab Visibility | Other settings |
| User | Collection - Add, Edit, View | Advanced | N/A |
| Collection Detail Custodian - Add, Edit, Delete, View | Collect | ||
| Collection Detail Custodian Target - Add, Edit, Delete, View | Collections | ||
| Collection Detail Custodian Target Result – Add, Edit, Delete, View | Custodial Target Status | ||
| Collection Detail Noncustodial Source – Add, Edit, Delete, View | Custodian Targets | ||
| Collection Detail Noncustodial Source – Add, Edit, Delete, View Entities | Entities | ||
| Collection Detail Request – Add, Edit, Delete, View | Matters | ||
| Collection Detail Source Instance – Add, Edit, Delete, View | Monitor | ||
| Collection Detail Source Type – Add, Edit, Delete, View | Non-Custodial Target Status | ||
| Collection Detail Summary – Add, Edit, Delete, View | Status Summary | ||
| Collection Matter – Add, Edit, View | |||
| Collection Run – Add, Edit, View | |||
| Collection Source Instance - View | |||
| Collection Source Instance Parameter - View | |||
| Collection Source Target Parameter Instance - View | |||
| Collection Source Target Parameter Type - View | |||
| Collection Source Type - View | |||
| Collection Source Type Parameter Type - View | |||
| CollectionSourceTypeCriteria - View | |||
| Collection Source Type Criteria Validator - View | |||
| Collection Source Type OAuth Definition - View | |||
| Custodian Target – Add, Edit, Delete, View | |||
| Custodian Target Generation Error – Add, Edit, Delete, View | |||
| Entity - View | |||
| Relativity Time Zone – Add, Edit, View | |||
| Processing Data Source – Add, Edit, View | |||
| Processing Error – Add, Edit, View | |||
| Processing Profile – Add, Edit, View | |||
| Processing Set – Add, Edit, View | |||
| Folder – Add, Edit, View | |||
| Administrator | CollectionSourceTypeCriteria – Edit, Delete, Secure, Add, View | Advanced | N/A |
| Custodian Target – Edit, Delete, Secure, Add, View | Collect | ||
| Noncustodial Target Generation Error – Edit, Delete, Secure, Add, View | Collection Admin | ||
| Collection Source Instance Parameter – Edit, Delete, Secure, Add, View | Collections | ||
| Collection Source Type Criteria Validator – Edit, Delete, Secure, Add, View | Custodial Target Status | ||
| Collection Detail Request – Edit, Delete, Secure, Add, View | Custodian Targets | ||
| Entity – Edit, Delete, Secure, Add, View | Entities | ||
| Collection Source Type Parameter Type – Edit, Delete, Secure, Add, View | Matters | ||
| Collection Source Type – Edit, Delete, Secure, Add, View | Monitor | ||
| Collection – Edit, Delete, Secure, Add, View | Non-Custodial Target Status | ||
| Collection Run – Edit, Delete, Secure, Add, View | Status Summary | ||
| Processing Error – Edit, Delete, Secure, Add, View | |||
| Collection Detail Custodian – Edit, Delete, Secure, Add, View | |||
| Processing Data Source – Edit, Delete, Secure, Add, View | |||
| Relativity Time Zone – Edit, Delete, Secure, Add, View | |||
| Collection Detail Custodian Target Result – Edit, Delete, Secure, Add, View | |||
| Collection Source Type OAuth Definition – Edit, Delete, Secure, Add, View | |||
| Processing Profile – Edit, Delete, Secure, Add, View | |||
| Collection Source Target Parameter Type – Edit, Delete, Secure, Add, View | |||
| Noncustodial Data Source Instance – Edit, Delete, Secure, Add, View | |||
| Collection Detail Custodian Target – Edit, Delete, Secure, Add, View | |||
| Collection Detail Source Type – Edit, Delete, Secure, Add, View | |||
| Collection Detail Source Instance – Edit, Delete, Secure, Add, View | |||
| Processing Set – Edit, Delete, Secure, Add, View | |||
| Collection Source Instance – Edit, Delete, Secure, Add, View | |||
| Custodian Target Generation Error – Edit, Delete, Secure, Add, View | |||
| Collection Detail Summary – Edit, Delete, Secure, Add, View | |||
| Collection Source Target Parameter Instance – Edit, Delete, Secure, Add, View | |||
| Collection Matter – Edit, Delete, Secure, Add, View | |||
| Collection Detail Noncustodial Target – Edit, Delete, Secure, Add, View | |||
| Folder – Edit, Delete, Secure, Add, View | |||
| Collection Detail Noncustodial Source – Edit, Delete, Secure, Add, View | |||
Export structured data
The feature permissions designated for Export structured data are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| User | Document – Add, Edit, View | Documents | Allow Export |
| Folder – Add, Edit, View | Import/Export Job | ||
| Import/Export Extraction Job – Add, Edit, View | |||
| Import/Export Job – Add, Edit, View | |||
| Production - View | |||
| Relativity Export Service Job – Add, Edit, View | |||
| Relativity Time Zone - View | |||
| Administrator | Document – Add, Edit, View, Secure, Delete | Documents | Allow Export |
| Folder – Add, Edit, View, Secure, Delete | Import/Export Job | ||
| Import/Export Extraction Job – Add, Edit, View, Secure, Delete | |||
| Import/Export Job – Add, Edit, View, Secure, Delete | |||
| Relativity Time Zone – View, Secure, Edit, Delete | |||
| Production – View, Secure, Edit, Delete | |||
| Relativity Export Service Job – Add, View, Edit, Secure, Delete | |||
Imaging
The feature permissions designated for Imaging are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| User | Document – Add, View | Documents | Image - mass |
| Imaging Profile – Add, View, Edit | Imaging Profiles | ||
| Imaging Set – Add, View, Edit | Imaging Sets | ||
| Native Type - View | |||
| Administrator | Document – Add, View, Edit, Secure, Delete | Documents | None |
| Imaging Profile – Add, View, Edit, Delete, Secure | Imaging Profiles | ||
| Imaging Set – Add, View, Edit, Delete, Secure | Imaging Sets | ||
| Native Type – View, Secure, Edit, Delete | |||
Legal hold
The feature permissions designated for Legal hold are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| Administrator | Custodian Role – Add, View, Edit, Delete | Legal Hold | Manage Object Types |
| Custodian Status – Add, View, Edit, Delete | Projects | Use Pivot/Chart | |
| Entity – Add, View | Communications | View All Audits | |
| Field – Add, View, Add Field Choice By Link | Reports | ||
| JobSchedule – Add, View, Edit, Delete | Question Responses | ||
|
Legal Hold Application Permissions:
|
Mailbox | ||
| Legal Hold Selector Communications – Add, View, Edit, Delete | Project Reminder | ||
| Legal Hold Selectors – View | Custodian Status Dashboard | ||
| Preservation Case – Add, View, Edit | Tasks | ||
| Preservation Case Source – Add, View, Edit, Delete | Legal Hold Libraries | ||
| Preservation Custodian Status – Add, View, Edit, Delete | Questionnaires | ||
| Preservation Custodian Target – Add, View, Edit, Delete | Questions | ||
| Preservation Hold Settings – Add, View, Edit, Delete | Attachments | ||
| Preservation Source – Add, View, Edit, Delete | Scheduled Reports | ||
| Preservation Target Discovery Status – Add, View, Edit, Delete | Legal Hold Admin | ||
| Preservation Target Filter – Add, View, Edit, Delete | Legal Hold Settings | ||
| Preserve Product – Add, View, Edit, Delete | Global Reminder | ||
| Preserve Product Source – Add, View, Edit, Delete | Preservation Hold Settings | ||
| Project – Add, View, Edit, Delete | Role | ||
| Project Health – Add, View, Edit, Delete | Custodian Portal Authentication Provider | ||
| Project Questionnaires – Add, View, Edit, Delete | Item Selectors | ||
| Project Questionnaires Report Sub View - View | Entities | ||
| Roles – Add, View, Edit, Delete | |||
| Scheduled Report – Add, View |
OCR
The feature permissions designated for OCR are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| User | OCR Set – Add, View | OCR Sets | Advanced & Saved Searches |
| OCR Profile - View | OCR Profiles | ||
| Production - View | |||
| Search - View | |||
| Administrator | OCR Set – Add, View, Secure, Edit, Delete | OCR Sets | Advanced & Saved Searches |
| OCR Profile – View, Add, Edit, Secure, Delete | OCR Profiles | ||
| Production – View, Secure, Edit, Delete | |||
| Search – View, Secure, Edit, Delete | |||
Preservation
The feature permissions designated for Preservation are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| User | Preservation – View, Edit, Delete | Data Preservation | |
| Preservation Data Service - View | |||
| Preservation Data Source - View | Preservation Hold Entity Status | ||
| Preservation Error – View, Edit, Delete | Preservation Hold Job | ||
| Preservation Hold Entity Status – View, Edit, Delete | Preservation Error | ||
| Preservation Hold – View, Edit, Delete | Preservation | ||
| Preservation Hold Job – View, Edit, Delete | Preservation Hold | ||
| Administrator | Custodian Role – View, Secure, Edit, Delete | None | |
| Custodian Status – View, Secure, Edit, Delete | |||
| Entity – View, Secure, Edit, Delete | |||
| Field – View, Secure, Edit, Delete | |||
| JobSchedule – View, Secure, Edit, Delete | |||
| Legal Hold Application Permissions – View, Secure, Edit, Delete | |||
| Legal Hold Selector Configurations – View, Secure, Edit, Delete | |||
| Legal Hold Selectors – View, Secure, Edit, Delete | |||
| Preserve Product – View, Secure, Edit, Delete | |||
| Preserve Product Source – View, Secure, Edit, Delete | |||
| Preservation – View, Edit, Delete, Secure | Data Preservation | ||
| Preservation Case – View, Secure, Edit, Delete | |||
| Preservation Case Source – View, Secure, Edit, Delete | |||
| Preservation Custodian Status – View, Secure, Edit, Delete | |||
| Preservation Custodian Target – View, Secure, Edit, Delete | |||
| Preservation Data Service – View, Edit, Delete, Secure | Preservation Error | ||
| Preservation Data Source – View, Edit, Delete, Secure | Preservation Hold Job | ||
| Preservation Error – View, Edit, Delete, Secure | Preservation Data Source | ||
| Preservation Hold – View, Edit, Delete, Secure | Preservation | ||
| Preservation Hold Entity Status – View, Edit, Delete, Secure | Preservation Data Service | ||
| Preservation Hold Job – View, Edit, Delete, Secure | Preservation Hold | ||
| Preservation Hold Settings – View, Secure, Edit, Delete | |||
| Preservation Source – View, Secure, Edit, Delete | |||
| Preservation Target Discovery Status – View, Secure, Edit, Delete | |||
| Preservation Target Filter – View, Secure, Edit, Delete | |||
| Project – View, Secure, Edit, Delete | |||
| Project Health – View, Secure, Edit, Delete | |||
| Project Questionnaires – View, Secure, Edit, Delete | |||
| Project Questionnaires Report Sub View – View, Secure, Edit, Delete | Preservation Hold Entity Status | ||
| Roles – View, Secure, Edit, Delete | |||
| Scheduled Report – View, Secure, Edit, Delete | |||
Production
The feature permissions designated for Production are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| User | Production – Add, View, Edit | Production Sets | Copy |
| Production Data Source – Add, View, Edit, Delete | Production Placeholder | Re-produce | |
| Production Information – Add, View, Edit | Production | ||
| Production Placeholder – Add, View, Edit | Case Admin | ||
| Administrator | Production – Add, View, Edit, Secure, Delete | Production Sets | View All Audits |
| Production Data Source – Add, View, Edit, Delete, Secure | Production Placeholder | Override Production Restrictions | |
| Production Information – Add, View, Edit, Secure, Delete | Production | Copy | |
| Production Placeholder – Add, View, Edit, Secure, Delete | Case Admin | Re-produce | |
Redact
The feature permissions designated for Redact are:
|
Role (Admin or User) |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| User | Document – View, Redact Document, Highlight Document, Local Access (Download, Copy Text) | None | None |
| Markup Set – Add, View | |||
| Redact – Add, Edit, Delete, View, Place/Edit Manual Redaction, Place/Edit Manual Highlight, Clear Markups, Unhide Excel Content, View Quality Control Panel, Accept/Reject Quality Control Entries, Native PDF Redactions, Native Excel Redactions, Image Restrictions | |||
| Redact Externally Redacted Native – Add, Edit, View | |||
| Redact Original Native – Add, Edit, View | |||
| Redact Produced Document – Add, Edit, View | |||
| Administrator | Document – View, Delete, Edit, Secure, Redact Document, Highlight Document, Local Access (Download, Copy Text) | Redact Projects | Convert Spreadsheet Markups |
| Markup Set – Add, View, Delete, Edit, Secure | Redact Original Native | ||
| Redact – Add, Edit, Delete, View, Secure, Place/Edit Manual Redaction, Place/Edit Manual Highlight, Clear Markups, Unhide Excel Content, View Quality Control Panel, Accept/Reject Quality Control Entries, Input Custom Redaction Text, Native PDF Redactions, Native Excel Redactions, Image Redactions | Redact External Markups | Revert Native Redactions | |
| Redact Externally Redacted Native – Add, Edit, View, Delete, Secure | Redact Settings | ||
| Redact Original Native – Add, Edit, View, Delete, Secure | Redact Redacted File | ||
| Redact Produced Document – Add, Edit, View, Delete, Secure | Redact Audits | Prepare Excel for Redact | |
| Redact Externally Redacted Native | |||
| Redact | |||
Sentiment analysis
The feature permissions designated for Sentiment analysis are:
|
Role |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| Administrator | Sentiment Analysis Job – Add, Edit, View, Delete, Secure | Sentiment Analysis Jobs | Detect Sentiment |
| Sentiment Result – Add, Edit, View, Delete, Secure | Sentiment Results | ||
| Documents |
Structured analytics
The feature permissions designated for Structured analytics are:
|
Role |
Object Security | Tab Visibility | Other settings |
|---|---|---|---|
| User | Alias - View | Structured Analytics Results | |
| Alias Domain - View | Documents | ||
| Analytics Profile - Add, Edit, View | Aliases | ||
| Entity - View | Repeated Content Filters | ||
| Repeated Content Filter – Add, Edit, View | Analytics Profiles | ||
| Structured Analytics Errors - View | Alias Domains | ||
| Structured Analytics Results – Add, Edit, View | Structured Analytics Set | Communication Analysis Widget | |
| Structured Analytics Set – Add, Edit, View | Entities | Email Thread Visualization | |
| Administrator | Alias – Add, Edit, View, Delete, Secure | Structured Analytics Results | |
| Alias Domain – Add, Edit, View, Delete, Secure | Documents | ||
| Field – View, Edit | Alias Domains | ||
| Analytics Profile – Add, Edit, View, Delete, Secure | Aliases | Email Thread Visualization | |
| Repeated Content Filter – Add, Edit, View, Delete, Secure | Analytics Profiles | ||
| Structured Analytics Errors - View | Entities | Communication Analysis Widget | |
| Structured Analytics Results – Add, Edit, View, Delete, Secure | Indexing & Analytics | Assign to Entity | |
| Structured Analytics Set – Add, Edit, View, Delete, Secure | Structured Analytics Set | Merge | |
